ad

Saturday, 14 November 2015

Paid web based proxy visitor!

Basic proxy visitor writte in PHP, allows you to fake useragent and referal.


Referals test:


Useragent and IP test:

Usage is pretty simple. Open proxy file and put proxy with port. One in each line. Open useragent file
and put useragent in double quotes, one in a line and do same with referal, no quotation is needed for referals, just one in a line


Then open index.php and update website variable with your website


At the bottom of page you will see what what proxy, referal and useragent is being used:


And finally upload the files to server! make sure you've curl enabled!
 
Price: $2 BTC only 1HbakPHgjY9sBAHudouVh31SixjhVyVdSt
Free now: http://bit.ly/1N6tDYy

Friday, 13 November 2015

Basics of automation with Javascript

I personally advice against botting. Tutorial for educational purpose only!

I'm show ya guys how to do three basic stuff.
1. Fill a form
2. Accept terms
2. Click submit button

Lets take this paidoffers website as an example http://www.paidoffers.co.uk/


See that signup button? lets click it using javascript, but before that make sure you've inspect element on! Right click anywhere, inspect element! for chrome you ask? figure it out yourself... please?

Alright next step:
We gonna select documenet then select that button, but to select the button we need its ID! go over the button, inspect element and see if you can see its ID.


See easy stuff! now lets select that,
document.getElementById("signup_button").click();

Oh shit! it actually clicked the button! thats right! Now we're here at the buttom and we need to fill that, hard? no way!


Now against same thing.. we need to get the IDs so we can fill it! .value method represents the value insite it.


document.getElementById("fullname").value="jones michael";
document.getElementById("email").value="jonesmichael@gmail.com";
document.getElementById("newPassword").value="123456789";
document.getElementById("newPasswordRepeat").value="123456789";


Alright that's getting too repetitive! lets move on. We need to check that checkbox too don't we? right to check the box we'll need to change the check property. To change checked property we target the element like usual, the target it's property .checked and set it to true? pretty damn simple huh?

document.getElementById("tos").checked = true;


Lastly we find the signup button ID and hit it!
document.getElementById("signup_button_b").click();

Alright guys! we're done make sure to share this tutorial if you liked it!

Block unwanted users from your website with apache

It doesn't take very long before some users start becoming a problem for the website itself.. to get rid of these type of users you can ban them by IP - ofcourse they can hide behind proxy, but here's an ways to block users from your website, for this you need access to .htaccess file. Most host give you the access, if you don't see no file, create one! .htaccess is a configuration file for apache! don't confuse it with php.ini file which's for PHP.

Type this in .htaccess file and restart your server(if it's localhost) if it's up in cloud just refresh the page for test!

deny from all IP.AD.D.RE.SS
 
And you're done! MAGIC!? To ban multiple IP's you can repeat the statement.

Wanna see it in action? Here:
[​IMG]

What about trying it on localhost? Save .htaccess file with this:
Deny all from 127.0.0.1

Detect Proxy with one line of code!

There's an eays to to detect proxy by making HTTP request to sites that have open API.

For exam this site http://check.getipintel.net/check.php?ip=IP_address takes IP address as a get ip parameter's value and returnd the likelyhood of it being proxy.

For example, I'm using a proxy on purpose to see what it returns.
http://check.getipintel.net/check.php?ip=166.62.97.241

If it returns 1, it's definitely a proxy, if it returns 0, it's a regular address and if it returns something in middle, for example, 0.08 there's chances it's a proxy too! and what about 0.5? right! we really cant tell in that case.

Good part about it is you can check user for proxy in your applications and take a decision whether to allow him or not.

You can read more about it on their offical website
http://getipintel.net/

Update. Thanks to Stewart for adding good reason why you'd want to use it.
1 - Protect your site from automated XSS / SQL Injection / Brute Force / Crawlers that steal your content -- Well that's just a load of crock since they don't use proxies. Also hackers tend to go via infected computers and not proxies

2 - Serve traffic / content to real users, not bots, which reduces server load (bot detection) -- Again bots run from their own servers not via proxies

3 - Stop bots from scraping your content or bots spamming your website -- See the previous two responses

4 - Prevent trolls / people that are trying to bypass a ban -- True but then it doesn't stop dynamic IP address allocation nor just going to shops and using the countless free WiFi spots available

5 - Greatly reduce fraud on e-commerce sites (anti-fraud) -- Again not really

Collect & Validate User Emails for marketing

A simple lightweight script that allows you to collect user emails by simply locking any content that user may be after. Simply post a preview of content on the front page and link it to locked page and watch valid email addresses roll in!

It's pretty simple to use:
1. Persuade user:
[​IMG]

2. Collect the mail
[​IMG]

Make sure email's valid
[​IMG]

User clicks the email(verifying email's valid) and gains access to premium page:
[​IMG]

You can also set email info in locked.php file:
[​IMG]

In index.php file you can set page info, it's best to spend some time here to persuade user:
[​IMG]

In key_checker.php file you can set the dowload link or you can display an help page with more info as desired:
[​IMG]


Price: $3 BTC 1HbakPHgjY9sBAHudouVh31SixjhVyVdSt
Free now: http://bit.ly/1IzPHfu
little script I wrote to collect user emails. It's pesuading user and collectig their emails.
Requiremets are PHP installed server.

It's pretty simple to use:
1. Persuade user:

2. Collect the mail

Make sure email's valid

User clicks the email(verifying email's valid) and gains access to premium page:

You can also set email info in locked.php file:

In index.php file you can set page info, it's best to spend some time here to persuade user:

In key_checker.php file you can set the dowload link or you can display an help page with more info as desired:

Demo:

Price: $3 BTC 1HbakPHgjY9sBAHudouVh31SixjhVyVdSt
You get any help you may need to set it up.

Saturday, 7 November 2015

Basic Linear Search Algorithm for web scraping and many other stuff

Basic Automation Algorithm

There's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulatedThere's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulated
There's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulated.
Basic Automation Algorithm

There's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulated.
Basic Automation Algorithm

There's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulated


Imaging you've a page and you intend to search for certain word. Your first step would be to either convert it to array or some organized format so it can be manipulated. There's plenty of techniques used in bots automation, they use different tricks and technique but the most common one is called Linear search. It's also quite useful in web scraping.

//Basic function declaration.
//Accepts two arguements, $array that we'll search in, and $target_word we wanna search for.
function find_word($array, $target_word) {
   
    // Here we being our basic for loop. We start 1 to 0, until i reaches arrays length, then we increment i
    for(var $i = 0; $i < $array.length; ++$i){
       
        // While looping it checks where $array[$i] <-- $i here represents a number that started from 0. And the whole expression
        // represents first array value. It it loops again, i will have value of 1 $array[1] will respresent 2nd value of array.
        // Then it checks if $array[$i] is equal the word we're looking for, if it finds the word, it will return the index or array position
        // where it was found
        if ($array[$i] == $target_word) {
            return $i;
        }
       
    }
   
    // If loop fails to find the word, it'll return -1, means it couldn't find the word.
    return -1;
}

find_word(["jon", "tom", "brown", 1, 0], "borwn");

Tuesday, 3 November 2015

How not to get your website hacked

The two most common type of attacks are:
  • SQL injection
  • XSS

SQL Injection(Senario):
  • Hacker can get access to premium section of the website
  • Can drop Database
  • Can echo all the data on screen
  • Can obviously steal confidential data and misue it
Picture from IBM

Prevention
Use PDO extention when making queries.
The PHP Data Objects (PDO) extension defines a lightweight, consistent interface for accessing databases in PHP. Each database driver that implements the PDO interface can expose database-specific features as regular extension functions. Note that you cannot perform any database functions using the PDO extension by itself; you must use a database-specific PDO driver to access a database server.

PDO provides a data-access abstraction layer, which means that, regardless of which database you're using, you use the same functions to issue queries and fetch data. PDO does not provide a database abstraction; it doesn't rewrite SQL or emulate missing features. You should use a full-blown abstraction layer if you need that facility.


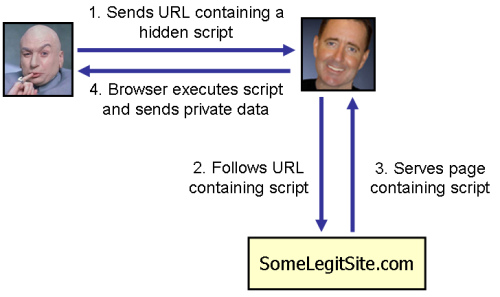
XSS(Senario):
  • Hack can steal other uses' cookies
  • Can change website look for all other uses
  • Can direct user to similar looking website
  • Can do pretty much anything that you would do with Javascript 
 Picture from moz.net

Prevention
Escape everything that you get from user, and escape everything that you display to user. This suspicious code will fail to directly execute on the browser. 

Tip: Always Encrypt your data. There's chances you may get hacked even all the preperation. You never want to give hacker access to pain data format.